Cybersecurity.
Without the business risk.
Offensive testing, compliance and continuous monitoring, built around Briskinfosec’s seven-layer security model.
Seven layers. One assessment. Evidence your team can act on.
Cyber risk management for financial services, healthcare, manufacturing, government, energy, telecom, technology and retail.
About Briskinfosec- 640+Client organizations
- 30+Countries served
- 5800+Security projects
- 9+Years in practice
Security services.
Assessment, operations and compliance expertise across your organization’s attack surface.
- 01
Web Application VAPT
Application testing for web vulnerabilities, authentication flaws and business logic risks.
- 02
Red Team Operations
Adversary simulation across digital, physical and human attack surfaces.
- 03
SOC as a Service
Continuous security monitoring, threat detection and incident response.
- 04
Governance & Compliance
ISO 27001, SOC 2, PCI-DSS, privacy and regulatory compliance support.
- 05
Cloud Security
AWS, Azure and GCP assessments covering infrastructure, identity and data.
- 06
AI/LLM Security Audit
Security assessments for AI models, LLM integrations and the pipelines behind them.
- 07
Mobile & API Security
Mobile apps, APIs and the authentication flows between them.
- 08
OT/SCADA Security
Industrial control systems, plant networks and operational technology.
- 09
Managed Security (MSSP)
An outsourced security function covering monitoring, response and advisory.
Seven layers between your data and the threat.
The data layer is the asset at the center. Six surrounding layers add testing, visibility, people and governance.
See the full model- 01
Governance
Policy and risk managementRisk management, privacy and compliance frameworks connect technical safeguards to business responsibilities.
- 02
Application
Apps, APIs and codeApplication testing, code review and secure development practices address risk across apps, APIs and code.
- 03
Perimeter
Boundary defenseRed Team Operations, access reviews and threat modeling examine how attackers could move through your defenses.
- 04
Human
People and awarenessAwareness training, phishing simulations and response exercises help teams recognize and respond to threats.
- 05
Infrastructure
Cloud, network and OTCloud, network and operational technology assessments examine the systems your business depends on.
- 06
Monitoring
Continuous visibilitySecurity operations, threat intelligence and continuous monitoring help expose activity across your environment.
- 07
Data
The core assetData is the core of Brisk’s seven-layer model. Every surrounding layer exists to help protect it.
How an assessment runs.
A typical engagement moves from a scoped test to a validated report your team can act on.
Book a security assessment 01
Scope
Define the systems, the rules of engagement and the decision the assessment has to support.
- Assets and access
- Threat model
- Rules of engagement
 02
Test
Test the agreed surface with manual techniques, tooling and scenario-based attack paths.
- Web and API
- Cloud and identity
- Red team
 03
Validate
Reproduce findings, confirm severity and separate exploitable risk from scanner noise.
- Evidence review
- Business impact
- Retest plan
 04
Report
Deliver a prioritized plan your engineers can act on, with evidence your auditors can use.
- Executive summary
- Remediation guidance
- Compliance evidence
Accreditations.
About our credentials
CREST-approved company
Vulnerability assessment and penetration testing.
CERT-In empanelled auditor
Indian Computer Emergency Response Team.
Certified, registered, audited.
The management-system certifications and registrations behind our assessments, audits and compliance work.
Verify a client certificateISO 27001:2022
Information security management
Management system
ISO 9001:2015
Quality management
Management system
DUNS
Verified enterprise
Registration
CS/PTS
Security services licence
CS/PTS/C-202603-105
Trusted in more than 30 countries.
A selection of the organizations Briskinfosec has worked with, from banking and telecom to manufacturing and government.
See all clients
Client marks are reproduced from Briskinfosec's published client list.
Security technology.
Products for code assessment, security maturity, remote testing and governance.
- Code intelligence
LuraInsight
Offline AI-powered static application security testing, with no cloud dependency.
- Security maturity
bSAFE
An OWASP ASVS-based scorecard for assessing security maturity.
- Remote assessment
BriskBox
A remote penetration testing appliance that brings security assessment capabilities to your site.
- Security guidance
LURA Portal
AI-assisted cybersecurity guidance through the LURA Portal.
- GRC and privacy
Bantrix
Compliance, risk, vendor and privacy work in one shared workspace.
- All platforms
See the full product line
Explore products
Built for environments attackers target.
Briskinfosec works with security and technology teams in regulated, high-stakes sectors where downtime and data exposure carry real consequences.
Scope your sectorResearch & insights.
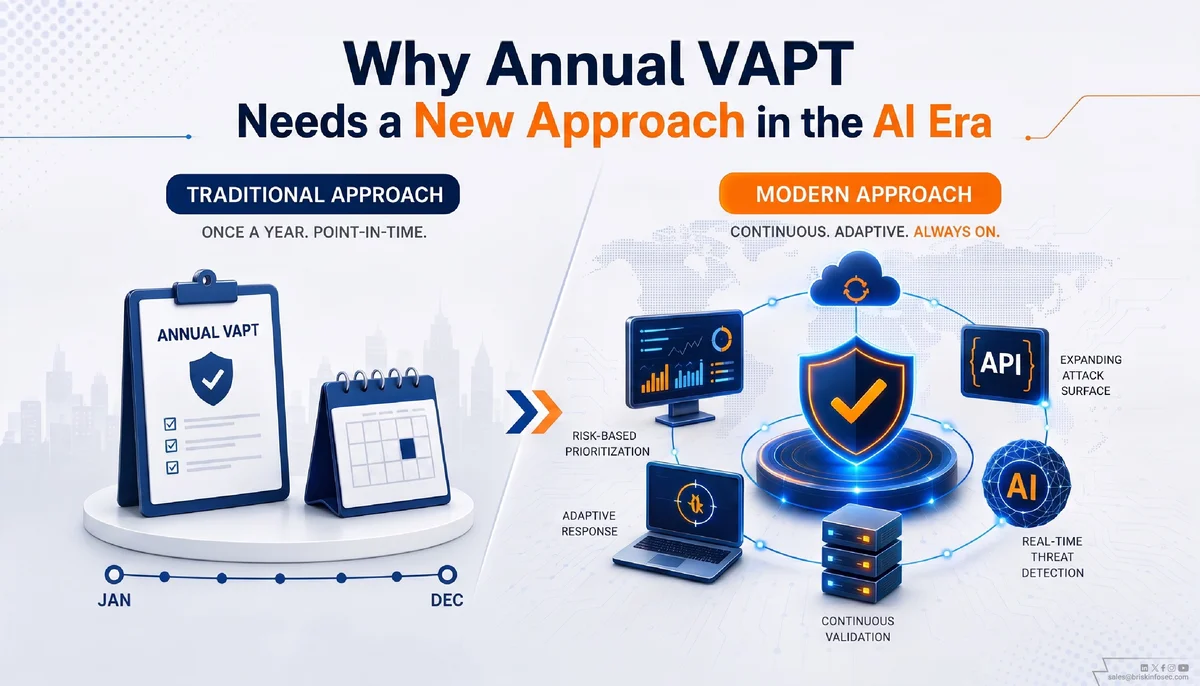
Read all insights
Testing a new application, preparing for an audit or reviewing an incident? Start with a scoped assessment.
Book a security assessmentQuestions worth asking.
Straight answers about scope, reporting and what happens after the assessment.
Ask us directlyWhat does a VAPT engagement cover?
A defined scope of applications, APIs, networks or cloud accounts, tested manually and with tooling, then validated and reported with severity and remediation guidance.
How is a red team different from a penetration test?
A penetration test targets a defined system. A red team simulates an adversary across people, infrastructure and access to test whether detection and response hold up.
Do you keep monitoring after the assessment?
Yes. SOC as a Service and MSSP cover continuous monitoring, threat detection and incident response, as an extension of your internal team.
Which compliance frameworks do you work with?
ISO 27001, SOC 2, PCI-DSS, HIPAA, GDPR, DPDPA, NIST CSF, IRDAI, ISO 22301, ISO 42001, IEC 62443 and ISO 21434, among others.
Where are you based?
Headquartered in Chennai, India, with an office in Dubai, UAE. Engagements are delivered on-site and remotely.
How do we start?
Book an assessment. We scope the environment, agree rules of engagement and share a proposal before testing begins.